As multi-cloud deployments turn into more frequent, organizations wrestle to maintain management over their critical keys. Dispersed keys lack clear possession or a scalable administration policy — both of that are made potential with Entrust KeyControl and Entrust nShield HSMs. Understanding RoT requires familiarity with several foundational ideas that govern how fashionable units establish security. Whether Or Not you’re innovating around safe boot flows, edge AI deployment, or heterogeneous compute frameworks, Eureka helps your team ideate sooner, validate smarter, and defend innovation sooner. Securing IoT units is important to protect the device makers reputation with customers and businesses. More And More additionally it is lined by regulation, regulation and requirements so safety can’t be added as an afterthought.

Root Of Belief In Ai And Agentic Techniques
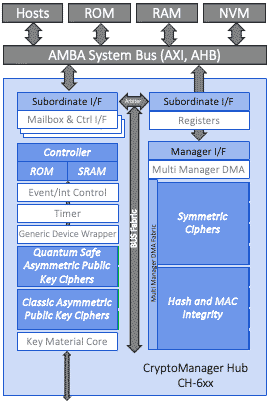
Sourcing the unique identifier (UID) and Hardware Unique Key (HUK) is a important utilization of an HRoT. The UID is used for device identification and communication with different system components. The HUK serves as the foundational cryptographic key used for deriving the other secret keys in a system. To best defend the UID/HUK as nicely as different saved secrets in the HRoT, anti-tamper measures have to be adequately designed in each bodily format and digital RTL. In a secure system, the RoT performs related capabilities, provisioning and storing the cryptographic root key.
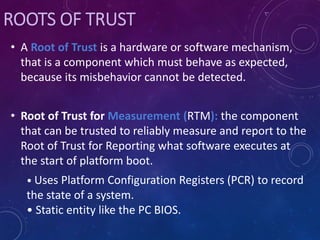
Data Safety Within The Cloud
- A critical facet of the Hardware Root of Belief is the entropy source to feed a device’s cryptographic algorithms.
- Connecting IoT devices to your network creates limitless choices for integration however also can create loopholes that can be exploited by hackers and other dangerous actors.
- This ROM contains the first-stage boot code and the general public key (or hash of the common public key) used to confirm the next stage.
- If any link in the chain fails verification, the process halts or flags an error, stopping compromised code from working.
The system generates an attestation report containing its PCR values, signed by a hardware-protected attestation key. If they match, the server trusts the gadget; if not, it could refuse entry or set off a remediation workflow. Offers distinctive, hardware-bound cryptographic identities (such as attestation keys) that permit devices to show their identity and resist spoofing during authentication. As growing numbers of IoT devices come on-line, most shall be uncovered to remote software program assaults and some will also need to mitigate hacks the place the attacker is physically present. IoT units that lack sufficient safety create alternatives for cybercriminals and hackers to brick units, take them over to type botnets, introduce unauthorized code, steal knowledge, or take advantage in different methods.
Choosing The Proper Hardware Root Of Trust
Roots of belief aren’t one-size-fits all, so before adopting one it is necessary to evaluate your security needs.
It provides an easy-to-use safety part applied by many of the world’s leading chip vendors. The PSA-RoT is normally supplied by the chip vendor and integrated of their Software Program Development Kits. It is accessible to platform and gadget software program through a excessive stage, easy-to-use software interface and consists of nine security capabilities designed to handle 10 key security goals. A root of trust supplies hardware-bound cryptographic identities and verifiable integrity measurements that systems can use to gauge http://www.sweetnovember.net/asset-protection-how-to-get-it-right.php trust before granting access. A root of trust offers cryptographic measurement and verification of the hardware and software setting during which AI workloads run, including agentic AI methods. A hardware root of trust may be embedded immediately into AI silicon (CPUs, GPUs, NPUs) to supply a bodily anchor for system integrity, and to guarantee that AI fashions, firmware, and information stay untampered with.
PSA Licensed offers organizations with an independent security evaluation that can be utilized to assist build in the proper degree of safety for linked units from the ground up. As Soon As the developer has determined the extent of safety required for their device by doing a risk mannequin, PSA Certified might help them select a chip with a suitably safe PSA-RoT. Before the gadget software program and different system software start to run, the gadget needs to boot and establish the software program running is authentic and has not been tampered with. This process is named trusted boot and is considered one of the essential capabilities of a well-designed RoT. Once the system has booted securely, certain operations want ongoing safety throughout runtime — cryptographic key operations, biometric processing, DRM, safe funds.